

100% Make in India - Digital Forensics Software
A powerful software designed to simplify evidence acquisition, examination, parsing, analysis, and reporting from Windows, macOS, storage drives.

Evidence Acquisition
Supports forensic imaging of logical volumes and physical drives in E01 and DD formats, including simultaneous imaging of multiple drives and the ability to assign acquisition priorities to selected cases or drives.

Cloud Image Integration
Support forensic imaging, acquisition, and examination of cloud data from Dropbox, Microsoft OneDrive, and Google Drive using valid user credentials for authenticated access.

NAS Imaging & Linux Recovery
Support forensic imaging of online and offline NAS storage in E01 and DD formats, along with direct data recovery from Linux drives across supported file systems.

Investigate Digital Artifacts
Support seamless loading, examination, and analysis of disk images, memory dumps and other digital evidence, with compatibility for EX01, E01, BIN, DD, AFF4-L, AFF, ZIP, TAR, and Virtual Images

Hash Validation
Supports MD4, MD5, SHA256, SHA512, Keccak_256, and Keccak_512 algorithms — dynamic hash generation in an easy-to-navigate HTML view. for both imaging reports and final artifact reports with multiple format.

File Search & Tagging
Support property-based file searching using file name, other metadata attributes, along with customizable evidence tags and color-coded labels for easy identification and case organization.
Supported Hash Algorithms
Supported Hash Algorithms
Comprehensive Feature Set
Advanced complete drive forensic acquisition, examination, analysis, and extractions in a single software
Artifacts Recovery & Visualizations
- Multimedia Extraction recovers deleted, lost, or inaccessible photos, videos, audio, and other evidence.
- Email Extraction recovers and analyzes deleted or inaccessible emails, attachments, and mailbox data.
- Cloud Data Extraction recovers and examines supported data from cloud storage and synced sources.
- Unknown Dataset Analysis identifies, classifies & analyzes unstructured datasets to uncover digital evidence.
Supported File System
- Windows File Systems: FAT12, FAT16, FAT32, exFAT, NTFS
- Mac File Systems: Mac File Systems: HFS, HFS+, APFS
- Linux File Systems: EXT2, EXT3, EXT4
- NAS File Systems: BTRFS
- CD/DVD file systems: CDFS, UDF, and HFS
- Virtual Disks: VDMK, VHD, VHDX
Forensic Reporting
- Custom Report Fragment Size: Adjust report fragment size as required.
- Photo Preview in Reports: Include image previews directly in forensic reports.
- Evidence Detail Validation: Verify and validate evidence details within reports.
- Flexible Reporting Controls: Customize report content, format, and output options.
Forensic Imaging & Investigation
Report Samples
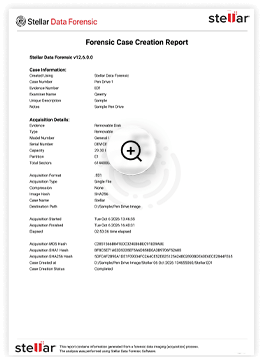
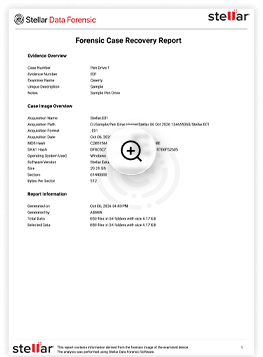
Explore sample forensic imaging and final investigation reports demonstrating evidence acquisition details, hash verification, examination results, and structured forensic reporting.
Technical Specifications
System Requirements


English


Windows 11 & 10
VICTORY PATH
Our Awards & Recognitions
We Found a Purpose to Serve, The Results Are Astonishing!
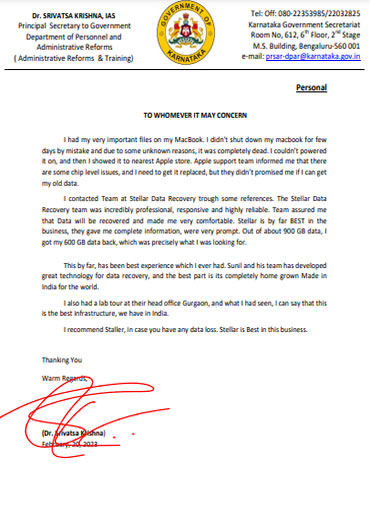

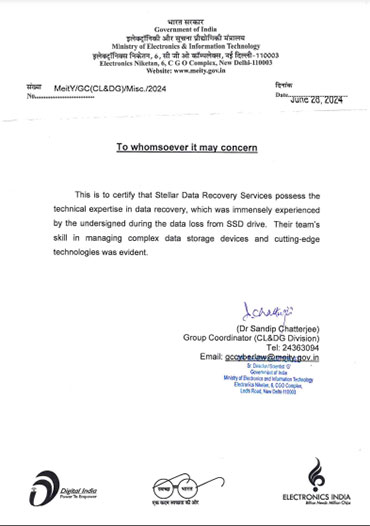
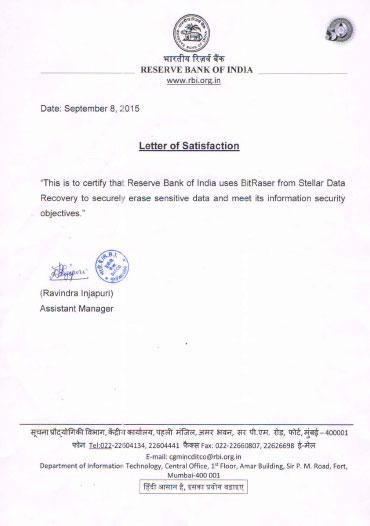
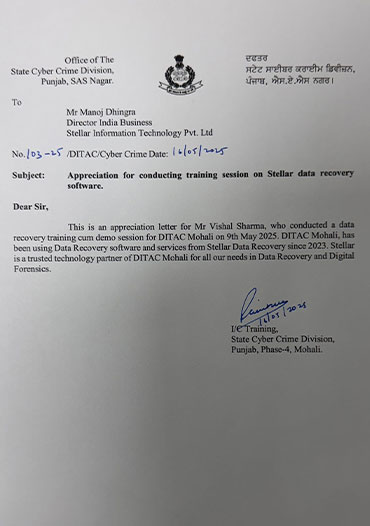
Trusted by Customers, Recognized by Brands
From individuals to global enterprises, our data recovery services are trusted for their reliability, security, and consistent performance.
You are in Expert hands!
With more than 3 million happy customers, Stellar is widely acknowledged as the No.1 data care provider for individuals and businesses.
*Reviews & Ratings are current as of March 2026.
Our Valued Customers
Trusted by thousands of customers for delivering reliable, secure, and professional data recovery.


Technology Proudly Developed in India
Stellar Data Care Products are now available on GeM. Exclusive offering for GOI
ADVANCED DATA RECOVERY INFRASTRUCTURE
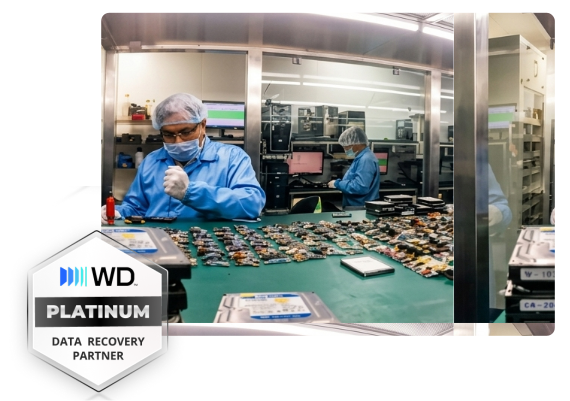
Stellar Class 100 Cleanroom Recovery
Physically damaged WD drives are safely handled in state-of-the-art ISO-certified Class 100 Cleanroom to prevent dust contamination and further damage.
 9350453636


FAQs
We have answers to the most common questions that our users ask.
Stellar Data Forensics for Drive is a digital forensic solution that helps investigators acquire, examine, and analyze data from hard drives, SSDs, computers, and supported network-attached storage (NAS) systems. It supports digital evidence collection and forensic investigation workflows.
Yes. The solution supports physical drive and logical volume imaging, including E01 and DD formats. It also supports hash generation to help verify image integrity and maintain the reliability of acquired digital evidence.
The solution supports hard disk drives (HDDs), solid-state drives (SSDs), and supported NAS storage. Its computer forensic capabilities cover Windows file systems such as NTFS and FAT, macOS file systems such as APFS and HFS+, Linux EXT file systems, and BTRFS for supported NAS environments.
Yes. The solution provides forensic reporting capabilities and supports hash generation for evidence verification. It also supports 30+ parallel imaging cases, along with case and drive prioritization, helping forensic laboratories manage multiple investigations efficiently.
Why Stellar® Is Global Leader
Delivering Industry-Leading Results For Over 30 Years
0M+
CUSTOMERS
0+
YEARS OF EXCELLENCE
0+
R&D ENGINEERS
0+
COUNTRIES
0+
PARTNERS
0+
AWARDS RECEIVED